Starter
For early-stage teams shipping their first compliance pentest.
—
- Any 1 asset (web, API, mobile or network)
- Manual pentest + report
- Unlimited retests
- Signed attestation letter
- Email support
Scantra Security · VAPT Services in India
Expert-led penetration testing services for web applications, APIs, mobile apps, networks and cloud. Get manual testing, AI-assisted discovery and clear remediation reports from one team, in India and beyond.
Reports aligned with
ISO 27001 · SOC 2 · PCI DSS · RBI · SEBI · DPDP Act · CERT-In guidelines
Share your assets and audit needs, then choose a 30-minute call.
Get a fixed scope, timeline and price on the call.
Security testing services
Looking for a penetration testing company in India? Scope web, API, mobile, internal and external network, or cloud security testing with one team.
Web application security testing of authentication, access control, sessions and business logic, beyond automated website scans.
CVSS-rated findings with evidence and remediation guidance.
Learn moreAPI VAPT for REST, GraphQL and SOAP endpoints, covering broken authorisation, data exposure and abuse.
Endpoint-level findings mapped to the OWASP API Top 10.
Learn moreAndroid and iOS apps, local storage, certificate handling and the APIs behind them.
Findings for the app and its backend in one report.
Learn moreInternal and external network testing of exposed services, segmentation and misconfiguration.
Prioritised list of exploitable network weaknesses.
Learn moreAWS, Azure and GCP configuration review plus testing of identity, storage and exposed workloads.
Cloud misconfigurations with clear remediation steps.
Learn moreAutomation supports discovery while manual testers validate vulnerabilities and assess real impact.
Human-verified findings with remediation priorities.
Learn moreVAPT scoped for ISO 27001, SOC 2, PCI DSS and Indian regulator requirements.
Audit-ready report you can share with auditors and buyers.
Learn moreWeb application security testing
Web application VAPT combines vulnerability assessment with manual penetration testing. Our web app pentest checks your real user roles, workflows and connected APIs using the OWASP Top 10 and Web Security Testing Guide, rather than relying on a scanner-only website assessment.
Vulnerability assessment and penetration testing
VAPT combines broad vulnerability discovery with hands-on security testing to verify exploitability. Scope both around your assets, audit requirements and delivery timeline.
Broad discovery of known weaknesses, missing patches and misconfiguration across your apps, servers and cloud. It tells you what might be wrong.
Manual, safe exploitation of those weaknesses to prove real impact, including chained and business logic issues tools cannot find. It tells you what an attacker can actually do.
Want the full VAPT view? See our VAPT company services or the India VAPT guide.
AI pentest
AI-assisted discovery and automation support asset mapping and repetitive checks. Human testers validate findings, examine business logic and assess attack paths. AI-assisted pentesting supplements expert testing; it does not replace it or guarantee that every vulnerability will be found.
How it works
A 30-minute call to map your web apps, APIs, mobile apps, networks and cloud, then a fixed written quote.
Automated discovery for breadth, then manual exploitation by testers across every asset in scope.
Executive summary plus technical findings with CVSS, evidence and fixes, in one report.
A findings walkthrough with your engineers and answers while they remediate.
Fixes are retested and the report is updated with resolved status.
Illustrative example
Scantra Security
Web application and API
Confidential. Client name redacted.
Reports
An executive view for leadership, customers and auditors. A technical view with evidence, reproduction steps and fixes for your developers.
Book a 30-minute call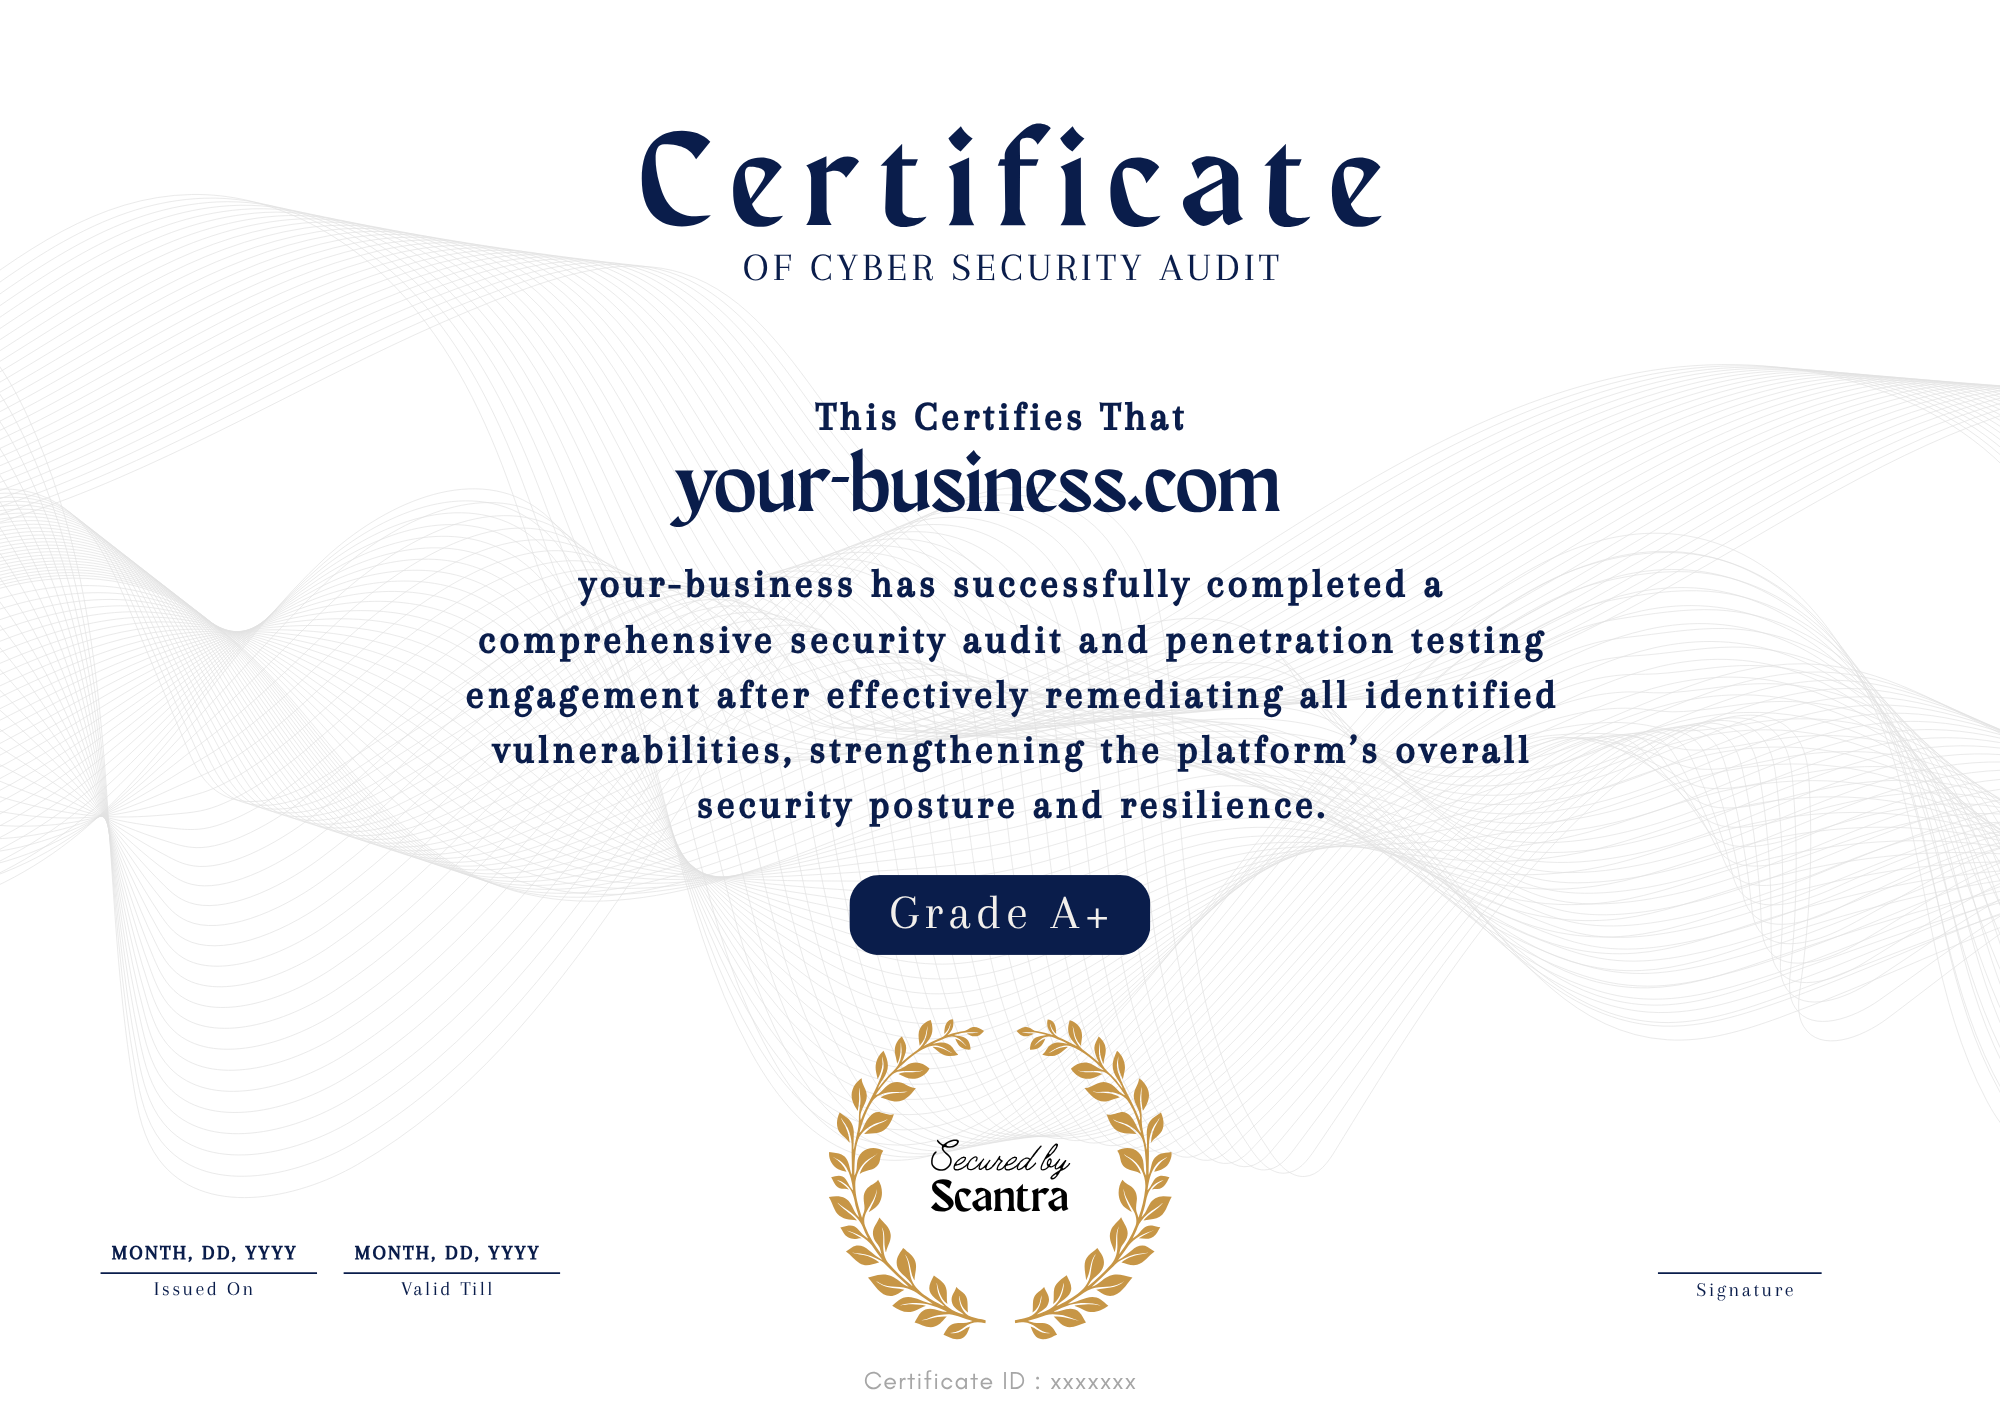
Book a call and we will walk you through a sample report and attestation letter.
Book a 30-minute callCompliance VAPT
Scope testing evidence for ISO 27001, SOC 2, PCI DSS and applicable Indian requirements. We also serve Indonesia and the UAE remotely. Testing supports an audit; it does not itself grant certification or regulatory approval.
Testing evidence for banks, NBFCs and payment businesses following RBI cyber security expectations.
VAPT reports for brokers and market intermediaries working to SEBI cyber resilience requirements.
Testing that shows how personal data is protected, supporting your DPDP Act security safeguards.
Reports aligned with CERT-In guidelines for security testing and reporting.
Penetration testing evidence for technical vulnerability management controls.
Third-party testing evidence for SOC 2 audits and customer security reviews.
Application and network penetration testing for PCI DSS testing requirements.
Pricing and quotes
Compare the plans below, then confirm a written quote based on your assets, user roles, integrations and audit scope. Combine web, API, mobile, network and cloud testing in one scoped engagement.
For early-stage teams shipping their first compliance pentest.
—
For scaling SaaS and FinTech teams.
—
For regulated, multi-region organisations with continuous needs.
Custom
Founders, CTOs and engineering leads on working with Scantra.
“Scantra Security brought a methodical, thoughtful approach to our security review. Communication stayed clear throughout, and the final recommendations were practical and easy for our team to prioritize.”

Rashmiranjan
Unifocus
“The engagement felt collaborative from kickoff through delivery. Scantra’s team explained its observations clearly, answered our questions promptly, and gave us actionable guidance to help strengthen our security practices.”
Rejji
Adonai Technowares
“We valued the professionalism and structure Scantra Security brought to the assessment. The team balanced technical depth with clear explanations, making the results useful to both technical stakeholders and decision-makers.”
Ramya
Clarity Benefit Solutions
“Scantra Security gave us a clear view of areas that deserved attention. Its organized process, responsive communication, and focused recommendations made it easier to translate the assessment into next steps.”
Arin
Finmark
“The team was thorough, approachable, and thoughtful in how it presented the findings. We appreciated that the recommendations were tied to practical risk reduction rather than simply a list of technical observations.”
Raja
Ahuda
“Working with Scantra Security was straightforward and well coordinated. The team kept us informed, addressed questions without delay, and delivered a report our team could use to plan remediation.”
Harsha
LWYD Interactive
“What stood out was the depth of the review and the care taken to explain why each issue mattered. Scantra’s team stayed engaged throughout and helped us understand the priorities clearly.”

Nikhil
Pixuate
“Scantra Security combined technical rigor with a professional, easy-to-work-with approach. The findings were communicated in plain language, helping us discuss improvements with the right people across the team.”
Rockson Samuel
Dental Reach
“The engagement was structured and supportive from start to finish. Scantra Security provided clear feedback, stayed available for follow-up discussions, and helped us approach remediation in a more organized way.”
BSS Bhopal IT Team
BSS Bhopal School
“Scantra Security took time to understand our priorities and kept the assessment focused. We appreciated the timely updates, detailed explanations, and practical direction provided at the end.”
Anmol
House of Agents
“The team demonstrated a disciplined testing process and communicated its observations with clarity. The organized reporting made it easier to review the results and align on corrective actions.”
Sandeep
IIT Kanpur
“The quality of the assessment and the clarity of the final report stood out. Scantra Security was responsive to our questions and gave us useful context for addressing the identified risks.”

Nagraj
Webstrail
“Scantra Security approached the work with care and professionalism. We particularly valued the constructive discussions around findings and the clear guidance on how to approach remediation.”
Faisal
BridgetIT
“This was a productive engagement with a team that was both thorough and responsive. The explanations were easy to follow, and the recommendations gave us a more confident basis for improving our security posture.”
Raj
Ahuda
“Scantra Security made a complex subject easier to act on. The team explained the significance of its findings clearly and provided a report that helped us focus attention where it would matter most.”
Sharendar
ToothTeller
“We appreciated the combination of technical diligence and smooth project coordination. Scantra’s team was approachable throughout and delivered insights that were clear, specific, and useful.”
Drishti
Hanomi India
“Scantra Security’s assessment was detailed without making the process difficult to follow. The team communicated professionally, responded quickly, and provided recommendations we could use to guide security improvements.”
Reema
BENEFLEX INDIA
“The engagement reflected strong technical attention and thoughtful communication. Scantra Security walked us through the findings in a clear, collaborative manner and helped us understand the best next steps.”
Prathvi Palekar
COCOSLABS INNOVATIVE SOLUTIONS
“Scantra Security was easy to coordinate with and thorough in its work. The final findings were well organized, and the team was available to clarify details so we could plan follow-up work effectively.”

Suman
Juego Studios
“The team brought a practical mindset to the assessment, focusing not only on identifying issues but also on explaining their implications. We appreciated the responsiveness and clarity of the remediation guidance.”
Sagar
Rebel Foods
“Scantra Security managed the engagement professionally and provided clear visibility from assessment through reporting. The findings were presented with useful context, supporting informed decisions about prioritization.”
Khalid
Allwyn North America
“The engagement was efficient, collaborative, and technically detailed. Scantra Security answered our questions thoughtfully and delivered clear recommendations that helped turn the assessment into an actionable plan.”
Meet
Nitro Commerce
“We valued the transparent communication and structured workflow throughout the engagement. Scantra’s report made the observations easy to understand and helped us identify the most important areas for follow-up.”

Bhavin
SaaSFlex
“Scantra Security brought a careful, professional approach and kept the process moving smoothly. The team explained its findings clearly and provided concrete recommendations without unnecessary jargon.”

Sharron
Fraganote
“From coordination to final delivery, the team was responsive and organized. Scantra Security gave us a clear understanding of the assessment outcomes and a practical foundation for further strengthening our security.”
Suchit
ECOMOTEL HOTEL
“The team combined a thorough review with clear, prompt communication. We appreciated the quality of the reporting and the way Scantra Security helped us understand which actions should come first.”

Harshil
Ace Turtle
“Scantra Security made it easy to collaborate at each stage. The team was open to questions, precise in its explanations, and helpful in translating the findings into sensible remediation priorities.”
Shirin
Ozi Technologies
“We had a positive experience with Scantra Security’s professionalism and attention to detail. The report was clear, the discussions were productive, and the recommendations offered a helpful route toward stronger security.”

Nupur
Vahdam Teas
“The engagement was managed with consistency and care. Scantra Security’s team was responsive when we needed clarification, and the final deliverable gave us a clear, prioritized view of improvements to consider.”

Kriti
StoreHippo
“Scantra Security demonstrated a disciplined approach and strong attention to detail. The team communicated outcomes clearly and provided practical observations that supported our internal review and next-step planning.”
Sergiy
Quilter
“We appreciated the team’s technical depth, discretion, and collaborative approach. Findings were explained with enough context to support meaningful follow-up, and the overall engagement was well coordinated.”
Chris Power
Hadrian
“Scantra Security approached the work with professionalism and thoughtful attention to detail. The team made time to clarify its observations and provided a clear basis for discussing potential security improvements.”

Kristen
BioAge Labs
“The assessment was thorough, with a reporting style that made the results easy to navigate. Scantra Security stayed responsive throughout and helped us connect technical findings to practical next steps.”

Ophir
DUST Identity
“We valued how accessible and organized the team was throughout the engagement. Scantra Security communicated its findings clearly and gave us recommendations that were straightforward to review and act on.”
Demi
Pika
“Scantra Security brought a calm, methodical approach to the review. The team was collaborative, answered questions promptly, and helped us understand how to turn the findings into meaningful improvements.”
Kartik
Blossom
“The team delivered a professional and well-structured engagement. Clear explanations, thoughtful follow-up, and practical reporting made the results easier to share internally and use for planning.”
Tyson
Avoca
“Scantra Security was thorough without losing sight of our timelines and priorities. The team’s communication was timely, and the final report made it easier to align on remediation work.”

Max
Sprinter Health
“We appreciated the careful analysis and candid, constructive communication from Scantra Security. The findings were presented clearly, with enough context to help our team make informed decisions about what to address.”

Brian
NewLimit
“The engagement was smooth from kickoff to closeout. Scantra’s team was responsive and detail-oriented, and the final recommendations gave us a practical framework for continued improvement.”
Tejas
HighTouch.io
“Scantra Security delivered a thoughtful assessment and a clear explanation of the outcomes. The collaborative approach made follow-up discussions productive and helped us plan security work with greater clarity.”

Justin
World Labs
FAQs
Our web application penetration testing covers authentication, authorisation, sessions, injection, business logic and the APIs behind your application. Testing follows the agreed scope, using the OWASP Top 10 and Web Security Testing Guide. You can also include Android and iOS apps, internal and external networks, and cloud environments in the same VAPT engagement.
VAPT combines a vulnerability assessment, which finds and lists weaknesses across your systems, with penetration testing, where testers safely exploit them to prove real impact. Penetration testing is the manual, exploit-driven part of VAPT.
In India, web application penetration testing typically ranges from ₹40,000 to ₹1,20,000 depending on size, user roles and complexity. Combined scopes with APIs, mobile, network or cloud are quoted together. You get a fixed price after the 30-minute scoping call.
Yes. You can scope your web app, the APIs behind it and your mobile apps in one engagement, with one timeline and one consolidated report.
Yes. Reports are structured to be used as evidence for ISO 27001, SOC 2, PCI DSS, RBI, SEBI and customer security reviews, with findings, risk ratings and retest status.
Yes. We test remotely for clients in Indonesia, the UAE and other countries. International engagements are quoted in USD.
Discuss your security testing needs, audit deadline and quote in one 30-minute call.